Cryptocurrency exchange Binance paused customer withdrawals across several blockchain networks on 29 October 2026 as security specialists opened an inquiry into a potential multi-billion-dollar Binance hack, after blockchain monitors detected rapid, unannounced outflows of digital tokens from the firm’s hot wallets into fresh addresses.
Key points
- Binance suspended withdrawals across multiple networks as internal teams investigate suspected unauthorised wallet drains.
- Stablecoin operators Tether and Circle intervened swiftly to freeze over $2.3 billion in transferred tokens.
- Blockchain trackers recorded up to $5.78 billion moving across flagged addresses, which would make the breach the largest in cryptocurrency history if confirmed.
- Company representatives insisted customer deposits remain secure while technical checks continue.
Outflows trigger emergency withdrawal freeze
Security alarms sounded across the digital asset sector on Thursday afternoon when on-chain surveillance services detected massive, coordinated transactions leaving storage facilities operated by Binance. The world’s largest cryptocurrency exchange moved quickly to stem further losses by locking outgoing transactions across multiple chains.
Ross O’Leary, a spokesperson for Binance, said the platform had temporarily suspended withdrawals across several networks as a precautionary safeguard while teams investigated the irregular activity. Technical personnel are reviewing transaction logs to identify how instructions were authorised.
A Binance spokesperson said that “user funds are completely safe” and noted that security engineers were working urgently to assess the network telemetry. The firm warned account holders to disregard unsolicited messages or requests for login credentials while official channels manage the incident.
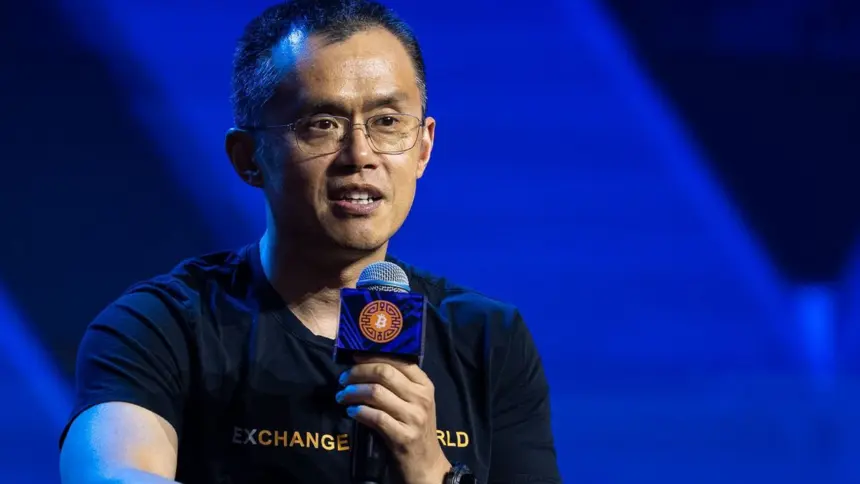
Changpeng Zhao, the founder and majority shareholder of Binance who stepped down from executive leadership in 2023, acknowledged the incident publicly on social platform X. Zhao said the unusual activity pointed towards a malicious breach, but told customers he expected all balances to be fully covered.
How the assets moved across the blockchain
Public ledger analysis revealed rapid drainage from internet-connected hot wallets used by the exchange to process routine daily trades. The automated transfers directed a vast mix of digital assets into an unlabelled destination address on the Ethereum network.
According to on-chain transaction records, an operational repository known as Binance 14 pushed roughly $2.53 billion split across 64 individual tokens in a single sweep. Less than half a minute later, a second Binance repository sent another $174.4 million to the same collector address.
A subsequent transaction transferred an additional 780 million units of USD Coin from a third corporate wallet, lifting the direct flow to the primary destination beyond $3.48 billion within minutes. The recipient account was quickly tagged on Etherscan with heist warnings to caution other market makers against processing incoming funds.
Broader clustering conducted through data compiled by Arkham Intelligence tracked 55 distinct addresses associated with the entity carrying the label binance-hacker-1029. Arkham logged approximately $5.78 billion across the cluster. The holdings featured large concentrations of liquid assets, comprising $1.77 billion of Tether alongside $823 million in USD Coin, as well as $1.44 billion in Bitcoin and $876 million in Ethereum. Analysts pointed out that the $5.78 billion figure reflected aggregate balances in the monitored wallets rather than an officially verified tally of stolen funds, and independent crypto researcher Molly White noted that market estimates near that ceiling were likely overstated.
Stablecoin issuers intervene to lock funds
The speed of the suspected breach triggered coordinated countermeasures from centralised stablecoin issuers, whose underlying smart contracts allow administrators to blacklist designated addresses and halt secondary movements.
Paolo Ardoino, chief executive of Tether, said the company “froze more than 1.567B USDT related to a potential Binance exchange hack.” The unilateral action isolated the largest single segment of the diverted dollar-pegged reserves before the controllers could convert them into privacy coins or route them through decentralised bridges.
Circle, the governing entity behind USD Coin, enacted similar countermeasures on its native smart contracts. Jeremy Allaire, chief executive of Circle, confirmed that his group locked more than $800 million in USDC associated with the flagged addresses and had engaged federal law enforcement agencies to assist the ongoing recovery effort.
The combined freeze locked up more than $2.3 billion in stable assets. Even with those assets restricted on-chain, significant volumes of unbacked tokens, including Bitcoin and native Ethereum, remain outside centralised administrative controls.
Market shock and historical comparisons
News of the potential compromise sent prices tumbling across major trading venues as market participants weighed the financial exposure of the sector’s central liquidity hub. Bitcoin dropped roughly 2.5 per cent to touch $79,098, while Ethereum shed 3.5 per cent to trade near $2,270. Binance’s native BNB token experienced the sharpest pullback, dropping 6.7 per cent to $705.
If forensic audits verify that attackers unlawfully siphoned anywhere near the upper estimate of $5.7 billion, the event will easily eclipse every previous theft in digital asset history. The existing benchmark occurred in February 2025, when the North Korean state-backed cyber group Lazarus infiltrated rival exchange Bybit and absconded with $1.4 billion in cryptocurrency.
The incident coincided with separate security stress elsewhere in the ecosystem. Earlier on Thursday, prediction protocol Polymarket temporarily suspended trading after hackers compromised third-party engineering partner DebugBear to plant a malicious wallet-draining script that siphoned roughly $2 million from web users.
What happens next
Binance has not yet detailed how the perimeter was penetrated, whether attackers compromised multi-signature signing keys, or whether internal credentials were leaked. Forensic teams are conducting an infrastructure audit across server environments before reopening customer withdrawals.
Exchange management stated that normal deposit and withdrawal functionality will resume once security verifications finish across all supported networks. Blockchain investigators and partner exchanges continue to monitor outbound transactions from the unblacklisted addresses to prevent perpetrators from liquidating the remaining assets.