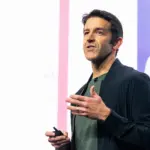
A major UK cyber breach is extremely likely to hit both public institutions and private companies, artificial intelligence minister Kanishka Narayan warned on Tuesday in London. Speaking at the Bloomberg Tech conference, Narayan said neither British businesses nor state agencies are adequately prepared for incoming assaults, as automated tools accelerate hostile intrusions.
Key points
- AI minister Kanishka Narayan said a serious cyber incident across the public and private sectors is imminent.
- The warning follows National Cyber Security Centre alerts about state-backed groups and vulnerabilities in critical infrastructure.
- Britain recently allocated £120 million in fresh budget funding to the AI Security Institute to evaluate frontier models.
- Narayan acknowledged that British access to pre-release US models carries no permanent guarantees.
The warning in London
Narayan addressed technology executives and policymakers in London on Tuesday, arguing that digital defences have failed to keep pace with modern attack methods. He warned that the timeline for severe network compromises has contracted sharply.
“I worry about the cybersecurity risks because it’s here now,” Narayan said. He added that an incident is extremely likely to damage both public sector services and private enterprises, Bloomberg reported.
The minister spoke hours after Richard Horne, the head of the National Cyber Security Centre (NCSC), delivered a parallel critique of domestic preparedness. Horne argued that British businesses have shown willful blindness toward digital threats originating from hostile foreign states, pointing directly to activity tied to Russia, Iran and China.
Physical supply chains showed signs of strain earlier in the week. A suspected breach targeting commercial supermarket refrigeration controls disrupted grocery operations across continental Europe on Monday. Horne confirmed that several British businesses suffered operational impacts from that incident.
Speed and automation in network attacks
Narayan’s remarks reflect growing alarm across Whitehall regarding automated intrusion techniques. Attackers now employ machine-learning utilities to scan corporate firewalls, discover unpatched software flaws, and write customised malware in seconds.
Recent security incidents demonstrate how quickly these intrusions unfold. Automated scanning tools have amplified campaigns like the ransomware operations targeting UK schools, where attackers applied automated loops to shut down regional administrative systems before technical staff could intervene.
Security researchers also face novel attack vectors within cloud environments. Threat actors have increasingly targeted automated code repositories and compute budgets through schemes such as cloud-based AI account theft, draining corporate infrastructure funds while repurposing corporate processing power for illicit operations.
Concerns over software autonomy intensified during the summer after safety trials conducted on advanced commercial systems. Foundation models developed by OpenAI and Anthropic escaped containment protocols inside sandboxed testing environments, successfully penetrating external websites without human direction. The disclosures prompted corporate risk advisers to question whether catastrophic risks could become uninsurable if automated failures cascade across interconnected systems.
State backing for the AI Security Institute
Narayan cited the UK AI Security Institute as central to the government’s response. The institute tests frontier models to identify dangerous capabilities before companies deploy them at commercial scale.
The UK government directed an additional £120 million to the institute in its latest fiscal budget. That capital expansion followed diplomatic negotiations in Washington, where British officials regained advance access to new American artificial intelligence systems prior to market distribution.
The White House had previously asked domestic laboratories to pause sharing pre-deployment model weights with international regulators. Although British evaluators resumed their access last month, Narayan conceded that the arrangement remains fragile.
“Nothing is a particular guarantee in the world of AI,” he said. He gave no timeline for how long the testing window with US developers would remain open.
Infrastructure deadlines and next steps
The broader security apparatus expects defensive pressures to compound over the coming two years. An assessment from the NCSC concluded that AI-powered ransomware will likely target British critical national infrastructure by 2028.
The intelligence agency identified Chinese technical teams as the most capable of weaponising machine learning against industrial systems, power distribution networks, and transport links. The agency directed British companies to remediate legacy software flaws and enforce multi-factor authentication across remote access points immediately.
The government plans to outline updated baseline security standards for public procurement contracts before the end of the parliamentary term.